
Pass with SC-200 Practice Materials 100% for sure

Study and Prepare with Microsoft SC-200 study material, That's Easy to pass With PracticeMaterial!
Last Updated: Oct 22, 2026
No. of Questions: 415 Questions & Answers with Testing Engine
Download Limit: Unlimited
The latest and reliable SC-200 Practice Materials with the best key knowledge is for easy pass!
Pass your real exam with PracticeMaterial latest SC-200 Practice Materials one-time. All the core knowledge of Microsoft SC-200 exam practice material are valid and reliable, compiled and edited by the experienced experts team, which can help you to deal the difficulties in the real test and pass the Microsoft SC-200 exam certainly.
100% Money Back Guarantee
PracticeMaterial has an unprecedented 99.6% first time pass rate among our customers.  We're so confident of our products that we provide no hassle product exchange.
- Best exam practice material
- Three formats are optional
- 10 years of excellence
- 365 Days Free Updates
- Learn anywhere, anytime
- 100% Safe shopping experience
- Instant Download: Our system will send you the products you purchase in mailbox in a minute after payment. (If not received within 12 hours, please contact us. Note: don't forget to check your spam.)
Microsoft SC-200 Practice Q&A's

- Printable SC-200 PDF Format
- Prepared by SC-200 Experts
- Instant Access to Download
- Study Anywhere, Anytime
- 365 Days Free Updates
- Free SC-200 PDF Demo Available
- Download Q&A's Demo
Microsoft SC-200 Online Engine

- Online Tool, Convenient, easy to study.
- Instant Online Access
- Supports All Web Browsers
- Practice Online Anytime
- Test History and Performance Review
- Supports Windows / Mac / Android / iOS, etc.
- Try Online Engine Demo
Microsoft SC-200 Self Test Engine

- Installable Software Application
- Simulates Real Exam Environment
- Builds SC-200 Exam Confidence
- Supports MS Operating System
- Two Modes For Practice
- Practice Offline Anytime
- Software Screenshots
Service quality shows after the sale, when you need an update, a re-send, or simply an answer. PracticeMaterial is structured around that after-sale reality, pairing 415 verified practice questions for the Microsoft Security Operations Analyst exam with a service package designed to cover every stage.
Microsoft SC-200 Exam Overview:
| Certification Vendor: | Microsoft |
|---|---|
| Exam Name: | Microsoft Security Operations Analyst |
| Exam Number: | SC-200 |
| Certificate Validity Period: | 1 year (renewal required) |
| Exam Price: | $165 USD |
| Real Exam Qty: | 40-60 |
| Related Certifications: | Microsoft Certified: Security Operations Analyst Associate |
| Passing Score: | 700 (scale of 100-1000) |
| Exam Format: | Multiple-choice, Case study, Multiple-select |
| Exam Duration: | 120 minutes |
| Available Languages: | Japanese, English, Chinese (Simplified), Korean |
| Sample Questions: | DOWNLOAD DEMO |
| Exam Way: | Online proctored or in-person testing center |
| Pre Condition: | Microsoft recommends having experience with Microsoft 365 Defender workloads, security operations, and incident response. Knowledge of Azure Active Directory, basic networking, and scripting is beneficial but not mandatory. |
| Official Syllabus URL: | https://learn.microsoft.com/en-us/certifications/exams/sc-200 |
Microsoft SC-200 Exam Syllabus Topics:
| Section | Weight | Objectives |
|---|---|---|
| Topic 1: Mitigate threats using Microsoft Defender for Endpoint | 25-30% | - Manage devices and monitor threats
|
| Topic 2: Mitigate threats using Microsoft 365 Defender | 25-30% | - Investigate and respond to threats in Microsoft 365 Defender
|
| Topic 3: Mitigate threats using Microsoft Defender for Identity | 15-20% | - Investigate and respond to identity threats
|
| Topic 4: Mitigate threats using Microsoft Defender for Cloud Apps | 20-25% | - Configure Microsoft Defender for Cloud Apps
|
SC-200 Exam: Frequently Asked Questions
This package includes 415 practice questions for the Microsoft Security Operations Analyst exam. Every answer is verified by an experienced team of experts, so you can trust what you study.
The Microsoft Security Operations Analyst exam requires a score of 700 (scale of 100-1000) to pass, and the official registration fee is $165 USD. Factoring in both before you start helps you plan the full cost of certification.
One purchase covers the full journey: three versions of the material (PDF, PC test engine, and online version), a free demo to try before buying, 365 days of free updates delivered automatically, and customer service you can reach whenever a question comes up. Nothing essential is sold separately.
The Microsoft Security Operations Analyst practice questions are organized around the official exam objectives. Key topics include:
- Mitigate threats using Microsoft 365 Defender (25-30%)
- Mitigate threats using Microsoft Defender for Cloud Apps (20-25%)
- Mitigate threats using Microsoft Defender for Identity (15-20%)
Keeping your revision mapped to these objectives makes every session productive.
Yes. Candidates who come back for additional certifications receive discounts when they buy further practice packages. If you already hold one of our products, ask our staff about the current returning-customer offer before your next purchase.
Microsoft recommends having experience with Microsoft 365 Defender workloads, security operations, and incident response. Knowledge of Azure Active Directory, basic networking, and scripting is beneficial but not mandatory.
You can confirm the current eligibility requirements on the official SC-200 exam page before you register.
The Microsoft Security Operations Analyst exam contains 40-60 questions, and you will have 120 minutes minutes to complete them. Training against the same volume of questions prepares both your knowledge and your pace.
Microsoft Security Operations Analyst Sample Questions:
You have a Microsoft Sentinel workspace.
You have a KQL query. The query returns Microsoft Sentinel incidents that are stored in the Securitylncident table and occurred during the last 90 days.
You need to create a Microsoft Sentinel workbook that will include a visualization of the query.
To what should you set Data source and Resource type for the workbook? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Correct Answer:

Explanation:
When you create a Microsoft Sentinel workbook that visualizes data retrieved using a Kusto Query Language (KQL) query, the workbook must use a data source that supports log analytics queries. According to Microsoft Sentinel and Azure Monitor documentation, Logs (Analytics) is the correct data source type for querying tables stored within a Log Analytics workspace, such as the SecurityIncident table. This table is where Microsoft Sentinel stores incident data.
In the workbook configuration, the Resource type determines which service the query context applies to.
Since you are querying Microsoft Sentinel incidents (not general Azure Monitor logs or metrics), you must set the resource type to Microsoft Sentinel. This ensures that the workbook is connected to Sentinel's analytics schema and can display visualizations (charts, metrics, timelines) based on Sentinel's native data tables.
Alternative resource types such as Log Analytics or Workspace could technically access the same data, but Microsoft Sentinel documentation recommends selecting Microsoft Sentinel when the workbook is designed for security operations and incident analysis. This provides tighter integration with the SOC dashboard experience, Sentinel permissions, and security insights views.
# Therefore, the correct selections are:
Data source: Logs (Analytics)
Resource type: Microsoft Sentinel
You have a Microsoft 365 E5 subscription that contains 200 Windows 10 devices enrolled in Microsoft Defender for Endpoint.
You need to ensure that users can access the devices by using a remote shell connection directly from the Microsoft 365 Defender portal. The solution must use the principle of least privilege.
What should you do in the Microsoft 365 Defender portal? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Correct Answer:

Explanation:
Box 1: Turn on Live Response
Live response is a capability that gives you instantaneous access to a device by using a remote shell connection. This gives you the power to do in-depth investigative work and take immediate response actions.
Box: 2 : Add a network assessment job
Network assessment jobs allow you to choose network devices to be scanned regularly and added to the device inventory.
Reference:
https://docs.microsoft.com/en-us/microsoft-365/security/defender-endpoint/respond-machine-alerts?
view=o365-worldwide
https://docs.microsoft.com/en-us/microsoft-365/security/defender-endpoint/network-devices?view=o365-worldwide
You need to implement the Defender for Cloud requirements.
What should you configure for Server2?
- A. an Azure resource tag
- B. the Microsoft Antimalware extension
- C. an Azure resource lock
- D. the Azure Automanage machine configuration extension for Windows
Correct Answer: A 🗳️
Explanation: Only visible for PracticeMaterial members. You can sign-up / login (it's free).
You need to configure the Microsoft Sentinel integration to meet the Microsoft Sentinel requirements. What should you do? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
Correct Answer:

Explanation: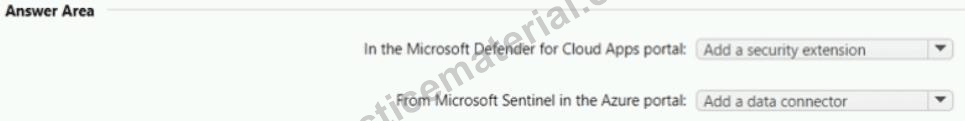
To integrate Microsoft Defender for Cloud Apps (MCAS) with Microsoft Sentinel, Microsoft's official SecOps and Sentinel documentation specifies a two-step configuration process.
In the Defender for Cloud Apps portal - You add a security extension to enable integration with external SIEM platforms. This action allows MCAS to forward its alerts, activities, and discovered app telemetry to other Microsoft or third-party security platforms. By adding the security extension, Defender for Cloud Apps is authorized to send data streams and alerts to Microsoft Sentinel through a supported API connection.
In Microsoft Sentinel (Azure portal) - You then add a data connector. Data connectors in Sentinel are predefined integration pipelines that bring in telemetry from Microsoft or external security solutions. The Microsoft Defender for Cloud Apps connector specifically ingests MCAS alerts and audit logs into Sentinel, where they can be correlated with other Microsoft Defender XDR signals, enabling unified detection and investigation across identity, endpoint, and cloud layers.
This integration approach adheres to Microsoft's principle of minimizing administrative effort by using native connectors rather than custom ingestion or log collector configurations. Once connected, Sentinel automatically normalizes MCAS alerts into its SecurityAlert and CloudAppEvents tables for rule creation, playbook automation, and incident correlation.
Therefore, the verified correct configuration is:
Defender for Cloud Apps: Add a security extension
Sentinel: Add a data connector
You have a Microsoft 365 E5 subscription that uses Microsoft Defender for Endpoint You need to identify any devices that triggered a malware alert and collect evidence related to the alert. The solution must ensure that you can use the results to initiate device isolation for the affected devices.
What should you use in the Microsoft 365 Defender portal?
- A. Incidents
- B. Investigations
- C. Advanced hunting
- D. Remediation
Correct Answer: B 🗳️
Explanation: Only visible for PracticeMaterial members. You can sign-up / login (it's free).
Viewing page 1 out of 83 pages.
Viewing questions 1-5 out of 415 questions.
Over 71500+ Satisfied Customers

So glad to find your site.
 Isabel
Liz
Naomi
Roxanne
With the help of PracticeMaterial SC-200 study guide, I was easily able to pass SC-200 exam on the first attempt.
Vera
Alvin
PracticeMaterial is the world's largest certification preparation company with 99.6% Pass Rate History from 71500+ Satisfied Customers in 148 Countries.

Our Clients


The best valid practice material for better understanding of the real exam. Learn and prepare efficiently with the products of PracticeMaterial.
Contact Us
From Monday to Saturday
Support: Contact now
If you have any question please leave me your email address, we will reply and send email to you in 12 hours.
Copyright © 2026 PRACTICEMATERIAL.COM. All rights reserved. All trademarks are the property of their respective owners and we don't provide actual questions from any vendor. Privacy Policy