

2023 Easy Success Microsoft AZ-800 Exam in First Try
Best AZ-800 Exam Dumps for the Preparation of Latest Exam Questions
Microsoft AZ-800 certification exam covers a wide range of topics related to administering Windows Server hybrid core infrastructure, including managing hybrid identities, managing virtual machines and containers, managing storage solutions, managing hybrid networking, and managing security and compliance. Administering Windows Server Hybrid Core Infrastructure certification exam is intended for IT professionals who are responsible for managing and administering hybrid environments of Windows Server, including on-premises and cloud-based infrastructure.
To pass the Microsoft AZ-800 exam, candidates need to demonstrate their ability to design, implement, and manage hybrid core infrastructure solutions that leverage both on-premises and cloud-based resources. They must have a deep understanding of Windows Server and Azure technologies, as well as experience with virtualization, networking, and storage. AZ-800 exam is ideal for IT professionals who are looking to advance their careers and demonstrate their expertise in managing hybrid environments. By passing AZ-800 exam, candidates can validate their skills and knowledge and differentiate themselves in the job market.
Earning the Microsoft AZ-800 certification demonstrates to potential employers that an IT professional is proficient in administering Windows Server hybrid core infrastructure. Administering Windows Server Hybrid Core Infrastructure certification can help IT professionals advance their careers and increase their earning potential. Additionally, it can help organizations ensure that their IT staff have the necessary skills and knowledge to manage their hybrid infrastructure effectively.
NEW QUESTION # 13
SIMULATION
You need to create a user named Admin1 in contoso.com. Admin1 must be able to back up and restore files on SRV1. The solution must use principle of the least privilege.
To complete this task, sign in the required computer or computers.
Answer:
Explanation:
NEW QUESTION # 14
Your network contains an Active Directory Domain Services (AD DS) domain named conioso.com.
You need to identify which server is the PDC emulator for the domain.
Solution: from Active Directory Users and Computers, you right-click contoso.com in the console tree, and then select Operations Master Does this meet the goal?
- A. Yes
- B. No
Answer: A
NEW QUESTION # 15
Your network contains an Active Directory Domain Services (AD DS) domain named adatum.com.

The domain contains a 'He server named Server1 and three users named User1. User2 and User), Server1 contains a shared folder named Share1 tha1 has the following configurations:
The share permissions for Share1 are configured as shown in the Share Permissions exhibit. (Click the Share Permissions tab.) Share! contains a file named Filel.txt. The advanced security settings for Filel.txt are configured as shown in the File Permissions exhibit. (Click the File Permissions tab.) For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: f ach correct selection is worth one point.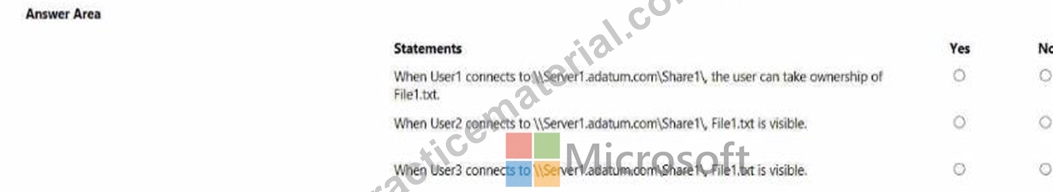
Answer:
Explanation:
NEW QUESTION # 16
You have a server that runs Windows Server and has the DHCP Server role installed. The server has a scope named Scope! that has the following configurations:
* Address range: 192.168.0.2 to 192.16B.1.2M . Mask 255.255.254.0
* Router: 192.168.0.1
* Lease duration: 3 days
* DNS server 172.16.0.254
You have 50 Microsoft Teams Phone devices from the same vendor. All the devices have MAC addresses within the same range.
You need to ensure that all the Teams Phone devices that receive a lease from Scope1 have IP addresses in the range of 192.168.1.100 to 192.168.1.200. The solution must NOT affect other DHCP clients that receive IP configurations from Scope1.
What should you create?
- A. scope options
- B. a scope
- C. a fitter
- D. a policy
Answer: D
Explanation:
Reference:
https://docs.microsoft.com/en-us/previous-versions/windows/it-pro/windows-server-2012-R2-and-2012/dn42504
NEW QUESTION # 17
You need to sync files from an on premises server named Server1 to Azure by using Azure File Sync.
You have a cloud tiering policy that is configured for 30 percent free space and 70 days.
Volume E on Server1 is 500 GB.
A year ago, you configured E:\Data on Server1 to sync by using Azure File Sync. The files that are visible in E:\Data are shown in the following table.
Volume E does NOT contain any other files.
Where are File1 and File3 located? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/windows-server/manage/windows-admin-center/azure/azure-file-sync
https://docs.microsoft.com/en-us/azure/storage/file-sync/file-sync-cloud-tiering-overview
NEW QUESTION # 18
You need to sync files from an on premises server named Server1 to Azure by using Azure File Sync.
You have a cloud tiering policy that is configured for 30 percent free space and 70 days.
Volume E on Server1 is 500 GB.
A year ago, you configured E:\Data on Server1 to sync by using Azure File Sync. The files that are visible in E:\Data are shown in the following table.
Volume E does NOT contain any other files.
Where are File1 and File3 located? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/windows-server/manage/windows-admin-center/azure/azure-file-sync
https://docs.microsoft.com/en-us/azure/storage/file-sync/file-sync-cloud-tiering-overview
NEW QUESTION # 19
Vou have an on-premises Active Directory Domain Services (AD DS} domain that syncs with an Azure Active Directory (Azure AD) tenant You have an on-premises web app named WebApp1 that only supports Kerberos authentication.
You need to ensure that users can access WebApp1 by using their Azure AD account. The solution must minimize administrative effort.
What should you configure? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
NEW QUESTION # 20
Your network contains two Active Directory forests and a domain trust as shown in the following exhibit.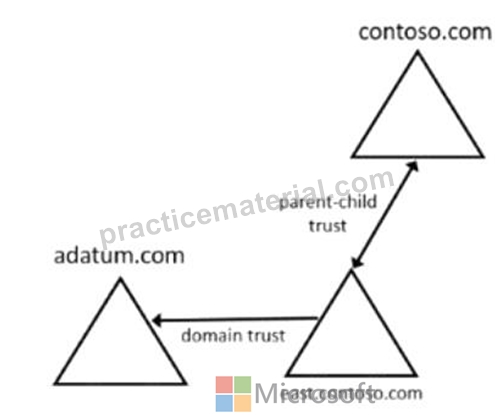
The domain trust has the following configurations:
* Name: adatum.com
* Type: External
* Direction: One-way. outgoing
* Outgoing trust authentication level: Domain-wide authentication
The forests contain the network shares shown in the following table.
For each of the following statements, select Yes if the statement is true. Otherwise, select No. NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation
NEW QUESTION # 21
Your network contains a single-domain Active Directory Domain Services (AD DS) forest named conto.com. The forest contains the servers shown in the following exhibit table.
You plan to install a line-of-business (LOB) application on Server1. The application will install a custom windows services.
A new corporate security policy states that all custom Windows services must run under the context of a group managed service account (gMSA). You deploy a root key.
You need to create, configure, and install the gMSA that will be used by the new application.
Which two actions should you perform? Each correct answer presents part of the solution.
NOTE: Each correct selection is worth one point.
- A. On DC1, run the New-ADServiceAccount cmdlet.
- B. ON DC1, run the Install-ADServiceAccount cmdlet.
- C. On DC1, run the Set_ADComputer cmdlet.
- D. On Server1, run the install-ADServiceAccount cmdlet.
- E. On Server1, run the Get-ADServiceAccount cmdlet.
Answer: A,D
NEW QUESTION # 22
You have an on-premises network that is connected to an Azure virtual network by using a Site-to-Site VPN.
Each network contains a subnet that has the same IP address space. The on-premises subnet contains a virtual machine.
You plan to migrate the virtual machine to the Azure subnet.
You need to migrate the on premises virtual machine to Azure without modifying the IP address. The solution must minim administrative effort.
What should you implement before you perform the migration?
- A. Azure virtual network peering
- B. Azure Application Gateway
- C. Azure Virtual Network NAT
- D. Azure Extended Network
Answer: D
Explanation:
Reference:
https://docs.microsoft.com/en-us/windows-server/manage/windows-admin-center/azure/azure-extended-network
NEW QUESTION # 23
You have an onpremises DNS server named Server1 that runs Windows Server. Server 1 hosts a DNS zone named fabrikam.com You have an Azure subscription that contains the resources shown in the following table.

Answer:
Explanation:
NEW QUESTION # 24
You have an on-premises Active Directory Domain Services (AD DS) domain that syncs with an Azure Active Directory (Azure AD) tenant The on-premises network is connected to Azure by using a Site-to-Site VPN. You have the DNS zones shown in the following table.
You need to ensure that names from (aDiifcam.com can be resolved from the on-premises network Which two actions should you perform? Each correct answer presents part of the solution, NOTE: Each correct selection Is worth one point
- A. Deploy an Azure virtual machine that runs Windows Server. Configure the virtual machine &s a DNS forwarder.
- B. Create a stub zone for fabrikam.com on DC1.
- C. Create a secondary zone for fabnlcam.com on DO.
- D. Deploy an Azure virtual machine that runs Windows Server. Modify the DNS Servers settings for the virtual network.
- E. Create a conditional forwarder for fabrikam.com on DC1.
Answer: A,E
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/private-link/private-endpoint-dns#on-premises-workloads-using-a-dns-fo
NEW QUESTION # 25
You need to sync files from an on premises server named Server1 to Azure by using Azure File Sync.
You have a cloud tiering policy that is configured for 30 percent free space and 70 days.
Volume E on Server1 is 500 GB.
A year ago, you configured E:\Data on Server1 to sync by using Azure File Sync. The files that are visible in E:\Data are shown in the following table.
Volume E does NOT contain any other files.
Where are File1 and File3 located? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/windows-server/manage/windows-admin-center/azure/azure-file-sync
https://docs.microsoft.com/en-us/azure/storage/file-sync/file-sync-cloud-tiering-overview
NEW QUESTION # 26
You are planning the implementation Azure Arc to support the planned changes. You need to configure the environment to support configuration management policies. What should you do?
- A. Create a hybrid runbook worker m Azure Automation.
- B. Hybrid Azure AD join all the servers.
- C. Deploy the Azure Connected Machine agent to all the servers.
- D. Deploy the Azure Monitor agent to all the servers.
Answer: C
NEW QUESTION # 27
SIMULATION
You need to collect errors from the System event log of SRV1 to a Log Analytics workspace.
The required source files are located in a folder named \\dc1.contoso.com\install.
To complete this task, sign in the required computer or computers.
Answer:
Explanation:
NEW QUESTION # 28
Your network contains an Active Directory Domain Services (AD DS) forest named contoso.com.
The forest root domain contains a server named server1.contoso.com.
A two-way forest trust exists between the contoso.com forest and an AD DS forest named fabrikam.com. The fabrikam.com forest contains 10 child domains.
You need to ensure that only the members of a group named fabrikam\Group1 can authenticate to server1.contoso.com.
What should you do first?
- A. Change the trust to a one-way external trust.
- B. Add fabrikam\Group1 to the local Users group on server1.contoso.com.
- C. Enable Selective authentication for the trust.
- D. Enable SID filtering for the trust.
Answer: C
Explanation:
Selective authentication restricts access over an external or forest trust to only those users in a trusted domain or forest who have been explicitly given authentication permissions to computer objects (resource computers) residing in the trusting domain or forest. This authentication setting must be manually enabled.
Note: When a two way Forest Trust is created between Forest A and Forest B, all domains in Forest A will trust all domains in Forest B and vice versa.
NEW QUESTION # 29
You have a Windows Server container host named Server1 that has a single disk.
On Server1, you plan to start the containers shown in the following table.
Which isolation mode can you use for each container? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/virtualization/windowscontainers/manage-containers/hyperv-container
NEW QUESTION # 30
Your network contains an Active Domain Services (AD DS) forest. The forest contains three domains.
Each domain contains 10 domain controllers.
You plan to store a DNS zone in a custom active Directory partition.
You need to create the Active Directory partition for the zone. The partition replicate to only four of the domain controllers.
What should you use?
- A. Active Directory Administrator Center
- B. dnscmd.exe
- C. Active Directory Sites and Services
- D. DNS Manager
Answer: A
NEW QUESTION # 31
You create an Azure virtual machine named Server1 that runs Windows Server.
Server1 has the disk configuration shown in the following exhibit.

Answer:
Explanation:
1 - Start Server1.
2 - Create and attach a new data disk.
3 - Shut down Server1.
NEW QUESTION # 32
You have 10 on-premises servers that run Windows Server.
You plan to use Azure Network Adapter to connect the servers to the resources in Azure.
Which prerequisites do you require on-premises and in Azure? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/windows-server/manage/windows-admin-center/azure/use-azure-network-adapter
NEW QUESTION # 33
You need to meet the technical requirements for VM1.
Which cmdlet should you run first? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
NEW QUESTION # 34
You have a Windows Server container host named Server1 and an Azure subscription.
You deploy an Azure container registry named Registry1 to the subscription.
On Server1, you create a container image named image1.
You need to store imager in Registry1.
Which command should you run on Server1 ? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/container-registry/container-registry-get-started-docker-cli?tabs=azure-cli#push-the-image-to-your-registry
NEW QUESTION # 35
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
Your network contains an Active Directory Domain Services (AD DS) domain named contoso.com.
You need to identify which server is the PDC emulator for the domain.
Solution: From Active Directory Domains and Trusts, you right-click Active Directory Domains and Trusts in the console tree, and then select Operations Master.
Does this meet the goal?
- A. Yes
- B. No
Answer: B
NEW QUESTION # 36
Your network contains an Active Directory Domain Services (AD DS) forest named contoso.com. The forest contains a child domain named east.contoso.com.
in the contoso.com domain, you create two users named Admin1 and Admin2.
You need to ensure that the users can perform the following tasks:
* Admin1 can create and manage Active Directory sites.
* Admin2 can deploy domain controller to the easl.conloso.com domain.
The solution must use the principle of least privilege.
To which group should you add each user? To answer, select the appropriate options in the answer area.
NOTE Each correct selection is worth one point.
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/windows-server/remote/remote-access/ras/multisite/configure/step-2-configure-the-multisite-infrastructure
NEW QUESTION # 37
Your network contains a single domain Active Directory Domain Services (AD DS) forest named contoso.com. The forest contains a single Active Directory site.
You plan to deploy a read only domain controller (RODC) to a new datacenter on a server named Server1. A user named User1 is a member of the local Administrators group on Server1.
You need to recommend a deployment plan that meets the following requirements:
Ensures that a user named User1 can perform the RODC installation on Server1 Ensures that you can control the AD DS replication schedule to the Server1 Ensures that Server1 is in a new site named RemoteSite1 Uses the principle of least privilege Which three actions should you recommend performing in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.
Answer:
Explanation:
Explanation
Application Description automatically generated with medium confidence
Box 1.
We need to create a site and subnet for the remote site. The new site will be added to the Default IP Site Link so we don't need to create a new site link. You configure the replication schedule on the site link.
Box 2.
When we pre-create an RODC account, we can specify who is allowed to attach the server to the prestaged account. This means that the User1 does not need to be added to the Domain Admins group.
Box3.
User1 can connect the RODC to the prestaged account by running the AD DS installation wizard.
Reference:
https://mehic.se/2018/01/02/how-to-install-and-configure-read-only-domain-controller-rodc-2016/
NEW QUESTION # 38
......
AZ-800 Study Material, Preparation Guide and PDF Download: https://www.practicematerial.com/AZ-800-exam-materials.html
AZ-800 Actual Questions 100% Same Braindumps with Actual Exam: https://drive.google.com/open?id=1U-7R2R_i6dEPeYe-lrw4SRtUzbiAP2b_
