

CAS-004 Exam Preparation Material with New CAS-004 Dumps Questions
CAS-004 2024 Training With 362 QA's
CompTIA CAS-004, also known as the CompTIA Advanced Security Practitioner (CASP+) exam, is a certification exam designed for IT professionals who have advanced-level knowledge and skills in cybersecurity. It is an internationally recognized certification that validates the technical knowledge and expertise required to conceptualize, design, and engineer secure solutions across complex enterprise environments.
NEW QUESTION # 214
Company A acquired Company B. During an audit, a security engineer found Company B's environment was inadequately patched. In response, Company A placed a firewall between the two environments until Company B's infrastructure could be integrated into Company A's security program.
Which of the following risk-handling techniques was used?
- A. Transfer
- B. Mitigate
- C. Accept
- D. Avoid
Answer: B
NEW QUESTION # 215
A developer implement the following code snippet.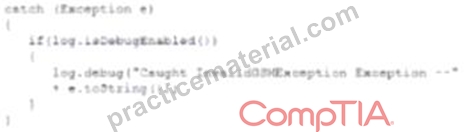
Which of the following vulnerabilities does the code snippet resolve?
- A. Missing session limit
- B. Information leakage
- C. SQL inject
- D. Buffer overflow
Answer: C
Explanation:
Explanation
SQL injection is a type of vulnerability that allows an attacker to execute malicious SQL commands on a database by inserting them into an input field. The code snippet resolves this vulnerability by using parameterized queries, which prevent the input from being interpreted as part of the SQL command. Verified References: https://www.comptia.org/training/books/casp-cas-004-study-guide ,
https://owasp.org/www-community/attacks/SQL_Injection
NEW QUESTION # 216
Company A is establishing a contractual with Company B.
The terms of the agreement are formalized in a document covering the payment terms, limitation of liability, and intellectual property rights. Which of the following documents will MOST likely contain these elements
- A. Company A-B NDA v03.docx
- B. Company A MSA v3.docx
- C. Company A MOU v1.docx
- D. Company A-B SLA v2.docx
- E. Company A OLA v1b.docx
Answer: D
NEW QUESTION # 217
A review of the past year's attack patterns shows that attackers stopped reconnaissance after finding a susceptible system to compromise. The company would like to find a way to use this information to protect the environment while still gaining valuable attack information.
Which of the following would be BEST for the company to implement?
- A. A SIEM
- B. A honeypot
- C. An IDS
- D. A WAF
Answer: B
NEW QUESTION # 218
Due to a recent acquisition, the security team must find a way to secure several legacy applications. During a review of the applications, the following issues are documented:
- The applications are considered mission-critical.
- The applications are written in code languages not currently
supported by the development staff.
- Security updates and patches will not be made available for the
applications.
- Username and passwords do not meet corporate standards.
- The data contained within the applications includes both PII and PHI.
- The applications communicate using TLS 1.0.
- Only internal users access the applications.
Which of the following should be utilized to reduce the risk associated with these applications and their current architecture?
- A. Use network segmentation to isolate the applications and control access.
- B. Update the company policies to reflect the current state of the applications so they are not out of compliance.
- C. Create a group policy to enforce password complexity and username requirements.
- D. Move the applications to virtual servers that meet the password and account standards.
Answer: D
NEW QUESTION # 219
A software development company is building a new mobile application for its social media platform. The company wants to gain its Users' rust by reducing the risk of on-path attacks between the mobile client and its servers and by implementing stronger digital trust. To support users' trust, the company has released the following internal guidelines:
* Mobile clients should verify the identity of all social media servers locally.
* Social media servers should improve TLS performance of their certificate status.
* Social media servers should inform the client to only use HTTPS.
Given the above requirements, which of the following should the company implement? (Select TWO).
- A. HSTS
- B. Quick UDP internet connection
- C. Private CA
- D. CRL
- E. DNSSEC
- F. OCSP stapling
- G. Distributed object model
Answer: A,F
Explanation:
OCSP stapling and HSTS are the best options to meet the requirements of reducing the risk of on-path attacks and implementing stronger digital trust. OCSP stapling allows the social media servers to improve TLS performance by sending a signed certificate status along with the certificate, eliminating the need for the client to contact the CA separately. HSTS allows the social media servers to inform the client to only use HTTPS and prevent downgrade attacks.
NEW QUESTION # 220
A technician is reviewing the following log:
Which of the following tools should the organization implement to reduce the highest risk identified in this log?
- A. SIEM
- B. NGFW
- C. NIPS
- D. DLP
Answer: D
NEW QUESTION # 221
An auditor Is reviewing the logs from a web application to determine the source of an Incident.
The web application architecture Includes an Internet-accessible application load balancer, a number of web servers In a private subnet, application servers, and one database server In a tiered configuration. The application load balancer cannot store the logs. The following are sample log snippets:
Which of the following should the auditor recommend to ensure future incidents can be traced back to the sources?
- A. Install a certificate signed by a trusted CA.
- B. Store the value of the $_SERVER['REMOTE_ADDR'] received by the web servers.
- C. Use stored procedures on the database server.
- D. Install a software-based HIDS on the application servers.
- E. Enable the x-Forwarded-For header al the load balancer.
Answer: E
Explanation:
The X-Forwarded-For (XFF) HTTP header field is a common method for identifying the originating IP address of a client connecting to a web server through an HTTP proxy or load balancer.
NEW QUESTION # 222
A security team received a regulatory notice asking for information regarding collusion and pricing from staff members who are no longer with the organization. The legal department provided the security team with a list of search terms to investigate.
This is an example of:
- A. legal hold.
- B. due intelligence
- C. e-discovery.
- D. due care.
Answer: C
Explanation:
E-discovery is a form of digital investigation that attempts to find evidence in email, business communications and other data that could be used in litigation or criminal proceedings. The traditional discovery process is standard during litigation, but e-discovery is specific to digital evidence. The evidence from electronic discovery could include data from email accounts, instant messages, social profiles, online documents, databases, internal applications, digital images, website content and any other electronic information that could be used during civil and criminal litigation.
NEW QUESTION # 223
In comparison with traditional on-premises infrastructure configurations, defining ACLs in a CSP relies on:
- A. containerization.
- B. serverless configurations.
- C. cloud-native applications.
- D. secure access service edge.
- E. software-defined netWorking.
Answer: E
Explanation:
Defining ACLs in a CSP relies on software-defined networking. Software-defined networking (SDN) is a network architecture that decouples the control plane from the data plane, allowing for centralized and programmable network management. SDN can enable dynamic and flexible network configuration and optimization, as well as improved security and performance. In a CSP, SDN can be used to define ACLs that can apply to virtual networks, subnets, or interfaces, regardless of the physical infrastructure. SDN can also allow for granular and consistent ACL enforcement across different cloud services and regions. Verified Reference:
https://www.techtarget.com/searchsdn/definition/software-defined-networking-SDN
https://learn.microsoft.com/en-us/azure/architecture/guide/networking/network-security
https://www.techtarget.com/searchcloudcomputing/definition/cloud-networking
NEW QUESTION # 224
A security architect needs to implement a CASB solution for an organization with a highly distributed remote workforce. One Of the requirements for the implementation includes the capability to discover SaaS applications and block access to those that are unapproved or identified as risky. Which of the following would BEST achieve this objective?
- A. Deploy endpoint agents that monitor local web traffic and control access according to centralized policy.
- B. Implement cloud infrastructure to proxy all user web traffic to enforce DI-P and encryption policies.
- C. Implement cloud infrastructure to proxy all user web traffic and control access according to centralized policy.
- D. Deploy endpoint agents that monitor local web traffic to enforce DLP and encryption policies.
Answer: C
NEW QUESTION # 225
An administrator at a software development company would like to protect the integrity of the company's applications with digital signatures. The developers report that the signing process keeps failing on all applications. The same key pair used for signing, however, is working properly on the website, is valid, and is issued by a trusted CA. Which of the following is MOST likely the cause of the signature failing?
- A. Each application is missing a SAN or wildcard entry on the certificate
- B. The certificate is set for the wrong key usage.
- C. The NTP server is set incorrectly for the developers
- D. The CA has included the certificate in its CRL.
Answer: B
Explanation:
The most likely cause of the signature failing is that the certificate is set for the wrong key usage. Key usage is an extension of a certificate that defines the purpose and functionality of the public key contained in the certificate. Key usage can include digital signature, key encipherment, data encipherment, certificate signing, and others. If the certificate is set for a different key usage than digital signature, it will not be able to sign the applications properly. The administrator should check the key usage extension of the certificate and make sure it matches the intended purpose. Verified Reference:
https://www.wintips.org/how-to-fix-windows-cannot-verify-the-digital-signature-for-this-file-error-in-windows-8-7-vista/
https://softwaretested.com/mac/how-to-fix-a-digital-signature-error-on-windows-10/
https://support.microsoft.com/en-us/office/digital-signatures-and-certificates-8186cd15-e7ac-4a16-8597-22bd163e8e96
NEW QUESTION # 226
Which of the following terms refers to the delivery of encryption keys to a CASB or a third-party entity?
- A. Key recovery
- B. Key escrow
- C. Key distribution
- D. Key sharing
Answer: C
Explanation:
Key Escrow is the process to store the key. Totally use key Escrow with CASB and third party but the deliver system is Key Distribution. In short escrow is method of storing and distribution is method of delivery.
https://csrc.nist.gov/glossary/term/key_distribution
https://jumpcloud.com/blog/key-escrow
NEW QUESTION # 227
Over the last 90 days, many storage services has been exposed in the cloud services environments, and the security team does not have the ability to see is creating these instance.
Shadow IT is creating data services and instances faster than the small security team can keep up with them. The Chief information security Officer (CIASO) has asked the security officer (CISO) has asked the security lead architect to architect to recommend solutions to this problem.
Which of the following BEST addresses the problem best address the problem with the least amount of administrative effort?
- A. Implement a CASB solution and track cloud service use cases for greater visibility.
- B. Capture all log and feed then to a SIEM and then for cloud service events
- C. Implement a user-behavior system to associate user events and cloud service creation events.
- D. Compile a list of firewall requests and compare than against interesting cloud services.
Answer: C
NEW QUESTION # 228
A development team releases updates to an application regularly.
The application is compiled with several standard open-source security products that require a minimum version for compatibility.
During the security review portion of the development cycle, which of the following should be done to minimize possible application vulnerabilities?
- A. The application development team should move to an Agile development approach to identify security concerns faster
- B. The change logs for the third-party libraries should be reviewed for security patches, which may need to be included in the release.
- C. The application should eliminate the use of open-source libraries and products to prevent known vulnerabilities from being included.
- D. The developers should require an exact version of the open-source security products, preventing the introduction of new vulnerabilities.
Answer: B
NEW QUESTION # 229
A developer wants to develop a secure external-facing web application. The developer is looking for an online community that produces tools, methodologies, articles, and documentation in the field of web-application security. Which of the following is the BEST option?
- A. CSA
- B. ICANN
- C. PCI DSS
- D. OWASP
- E. NIST
Answer: D
Explanation:
The Open Web Application Security Project (OWASP) is a group that monitors web attacks.
OWASP maintains a list of the top 10 attacks on an ongoing basis. This group also holds regular meetings at chapters throughout the world, providing resources and tools including testing procedures, code review steps, and development guidelines.
NEW QUESTION # 230
......
Quickly and Easily Pass CompTIA Exam with CAS-004 real Dumps: https://www.practicematerial.com/CAS-004-exam-materials.html
CompTIA CAS-004 Certification Exam Questions: https://drive.google.com/open?id=1AyU7pkhy-Z22WpDrITf_TxlB1esxtHP9
